← All OWASP awards

Distinguished Lifetime Members

Distinguished Lifetime Membership is the OWASP Foundation's highest honour, awarded to individuals whose sustained contributions have shaped the organisation and the wider application security community.

18 recipients in total

2026

No photo

Rob van der Veer

Distinguished Lifetime Members · 2026

2025

Andrew van der Stock

Andrew van der Stock

Distinguished Lifetime Members · 2025
Andrew has been involved with OWASP since near the beginning 25 years ago. He has been a project leader for several flagship projects, a chapter leader, an ex-Board member, and is currently the Executive Director of the OWASP Foundation.
linkedin.com
Christian Folini

Christian Folini

Distinguished Lifetime Members · 2025
When Christian Folini made his debut at the OWASP AppSec conference in Milan in 2007, he quickly found himself invited to share his insights on a panel discussing the emerging PCI DSS Web Application Firewall (WAF) requirements. During the years, he has evolved into a cornerstone of the open-source WAF community. As the author of the second edition of the ModSecurity Handbook he is one of the go-to experts for all things rule language. Folini introduced groundbreaking concepts such as the OWASP CRS Paranoia Levels and the notion of strict siblings. His innovative spirit led to the design of the CRS plugin architecture and the inception of the CRS dev-on-duty program. Moreover, Folini played a key role in transitioning ModSecurity to become a part of the OWASP Foundation. Beyond his contributions to OWASP, Christian Folini is a member of the steering committee for the Swiss National Cyber Strategy. He is also the public face of the Swiss Cyber Storm conference and continues to shape the cybersecurity landscape both in Switzerland and on a global level.
linkedin.com
Josh Grossman

Josh Grossman

Distinguished Lifetime Members · 2025
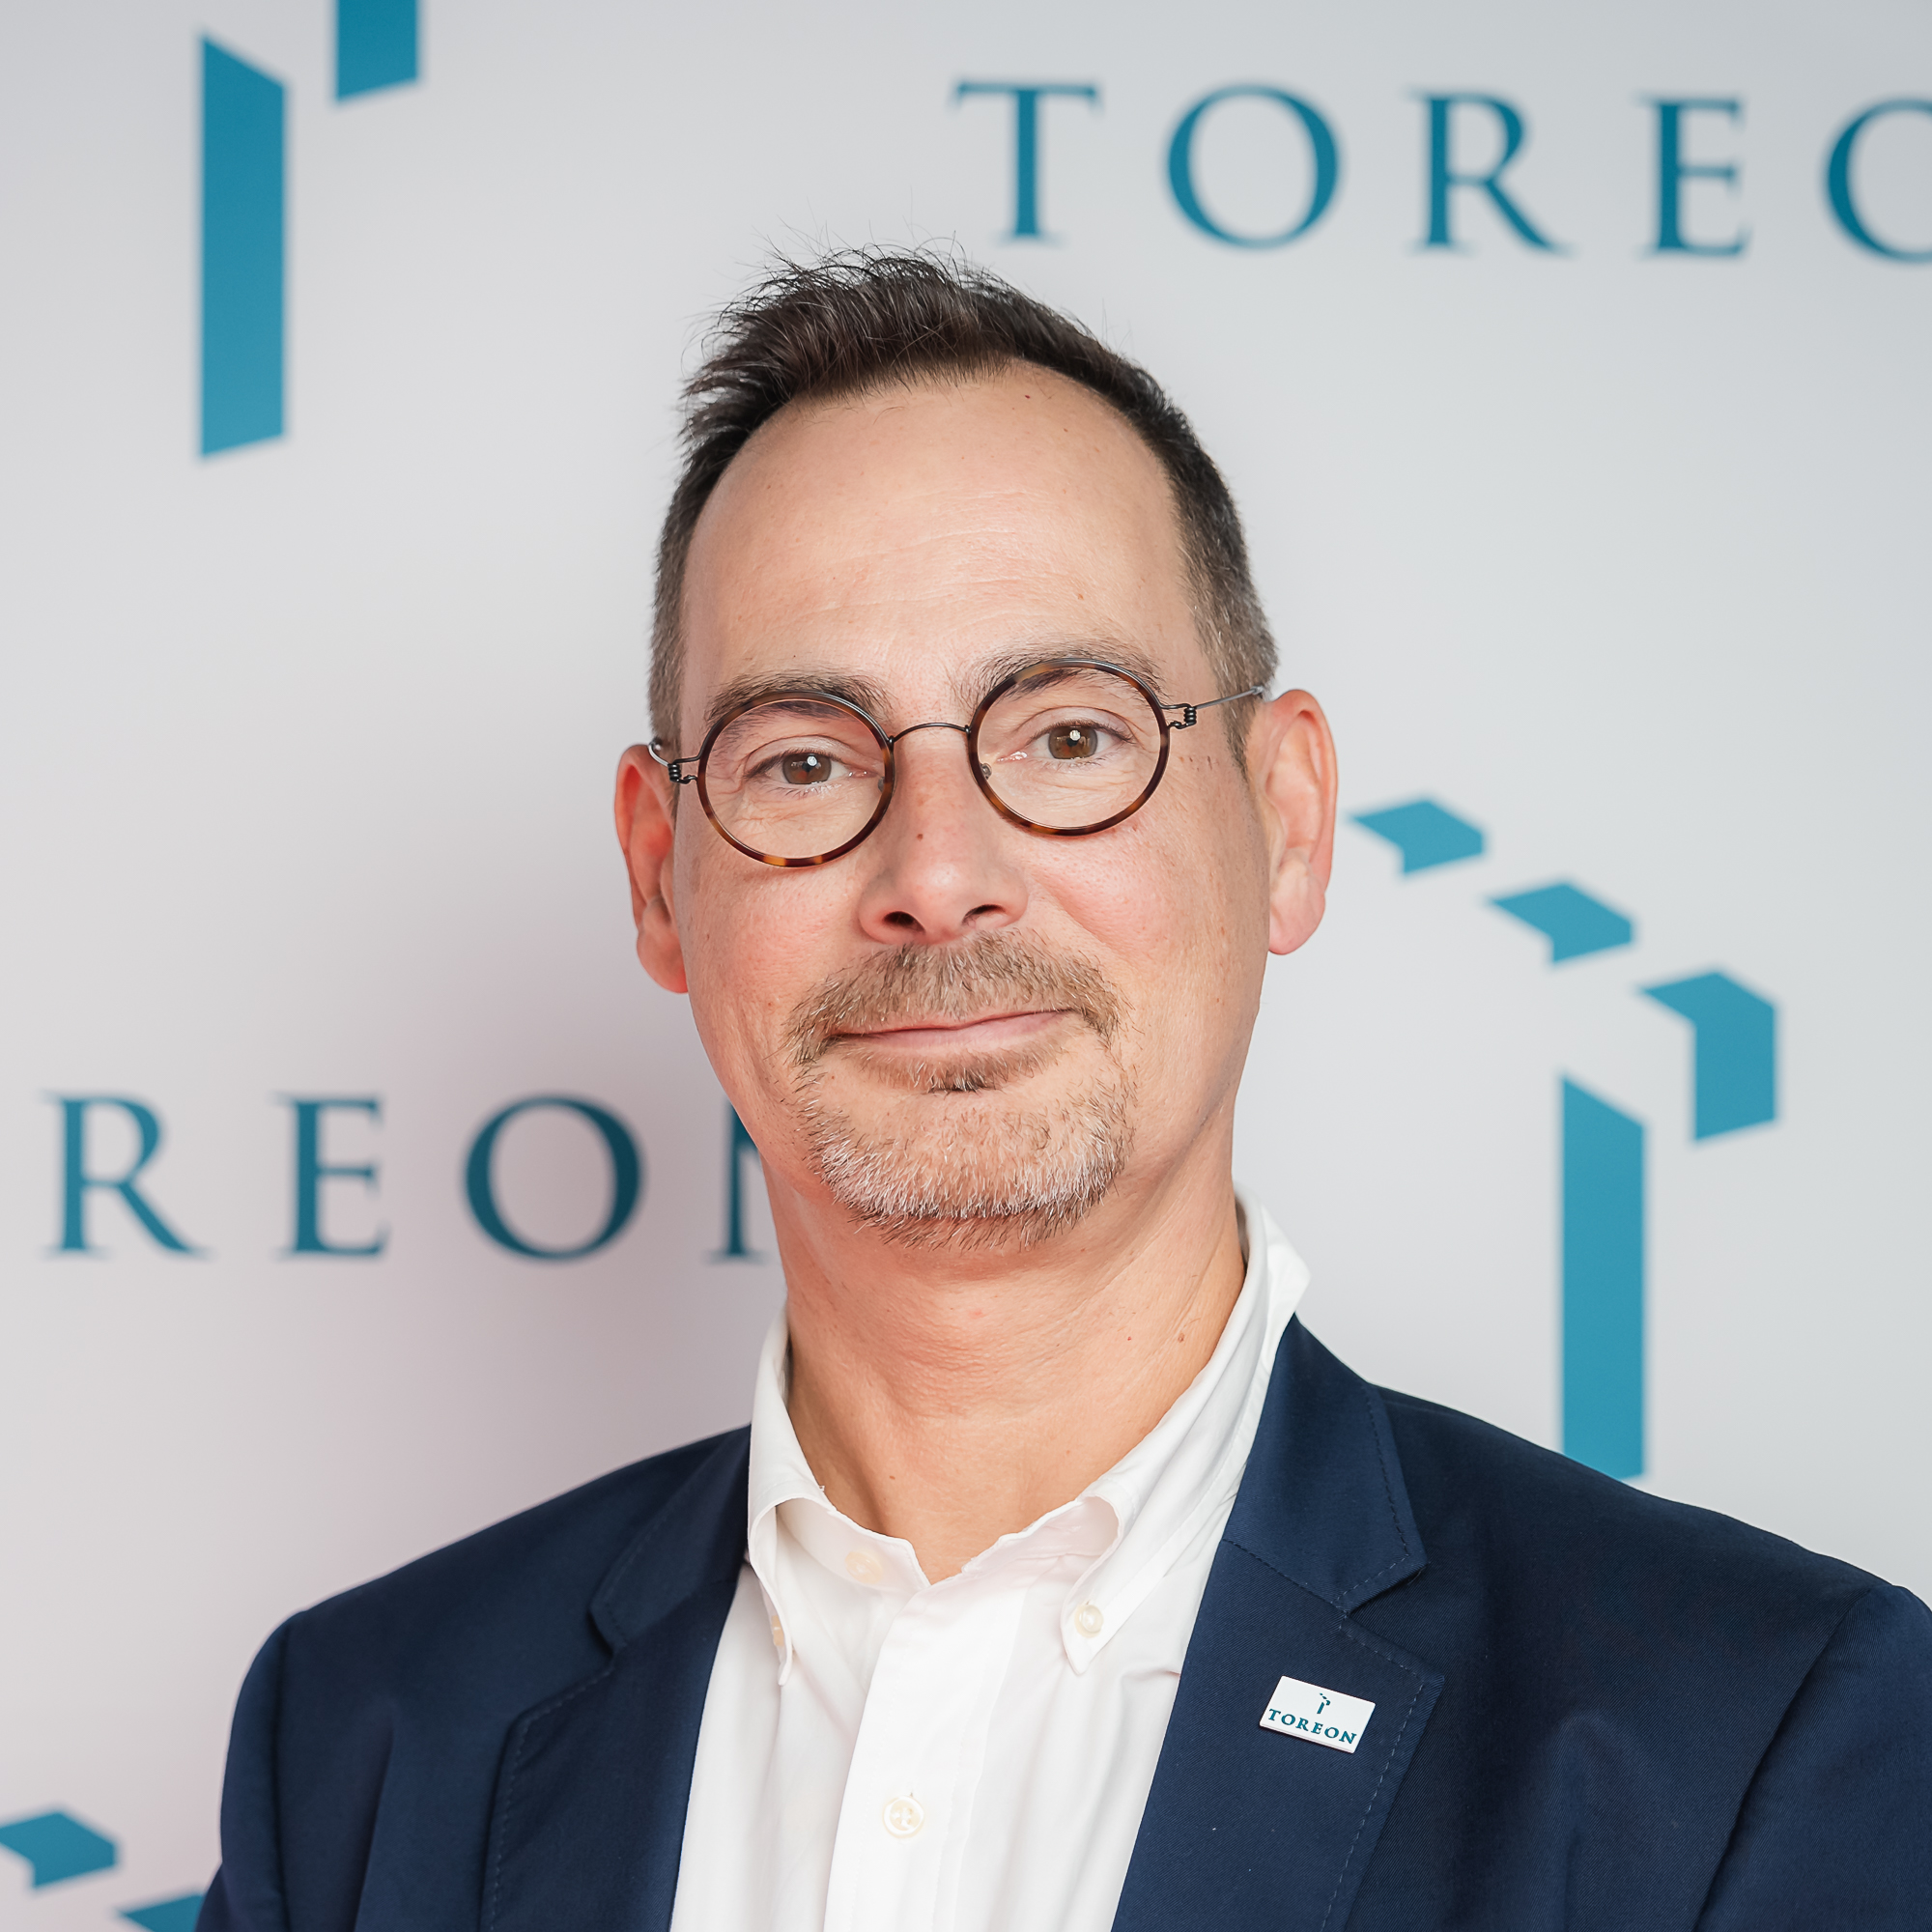
Outside of his day job as an AppSec practitioner, Josh has been involved with OWASP in many different roles. This includes serving as a co-leader of the Israel chapter (and co-organizing the legendary AppSecIL conference), serving as a member of the events committee, and also working as a co-leader of the OWASP ASVS project.
linkedin.com
Seba Deleersnyder

Seba Deleersnyder

Distinguished Lifetime Members · 2025
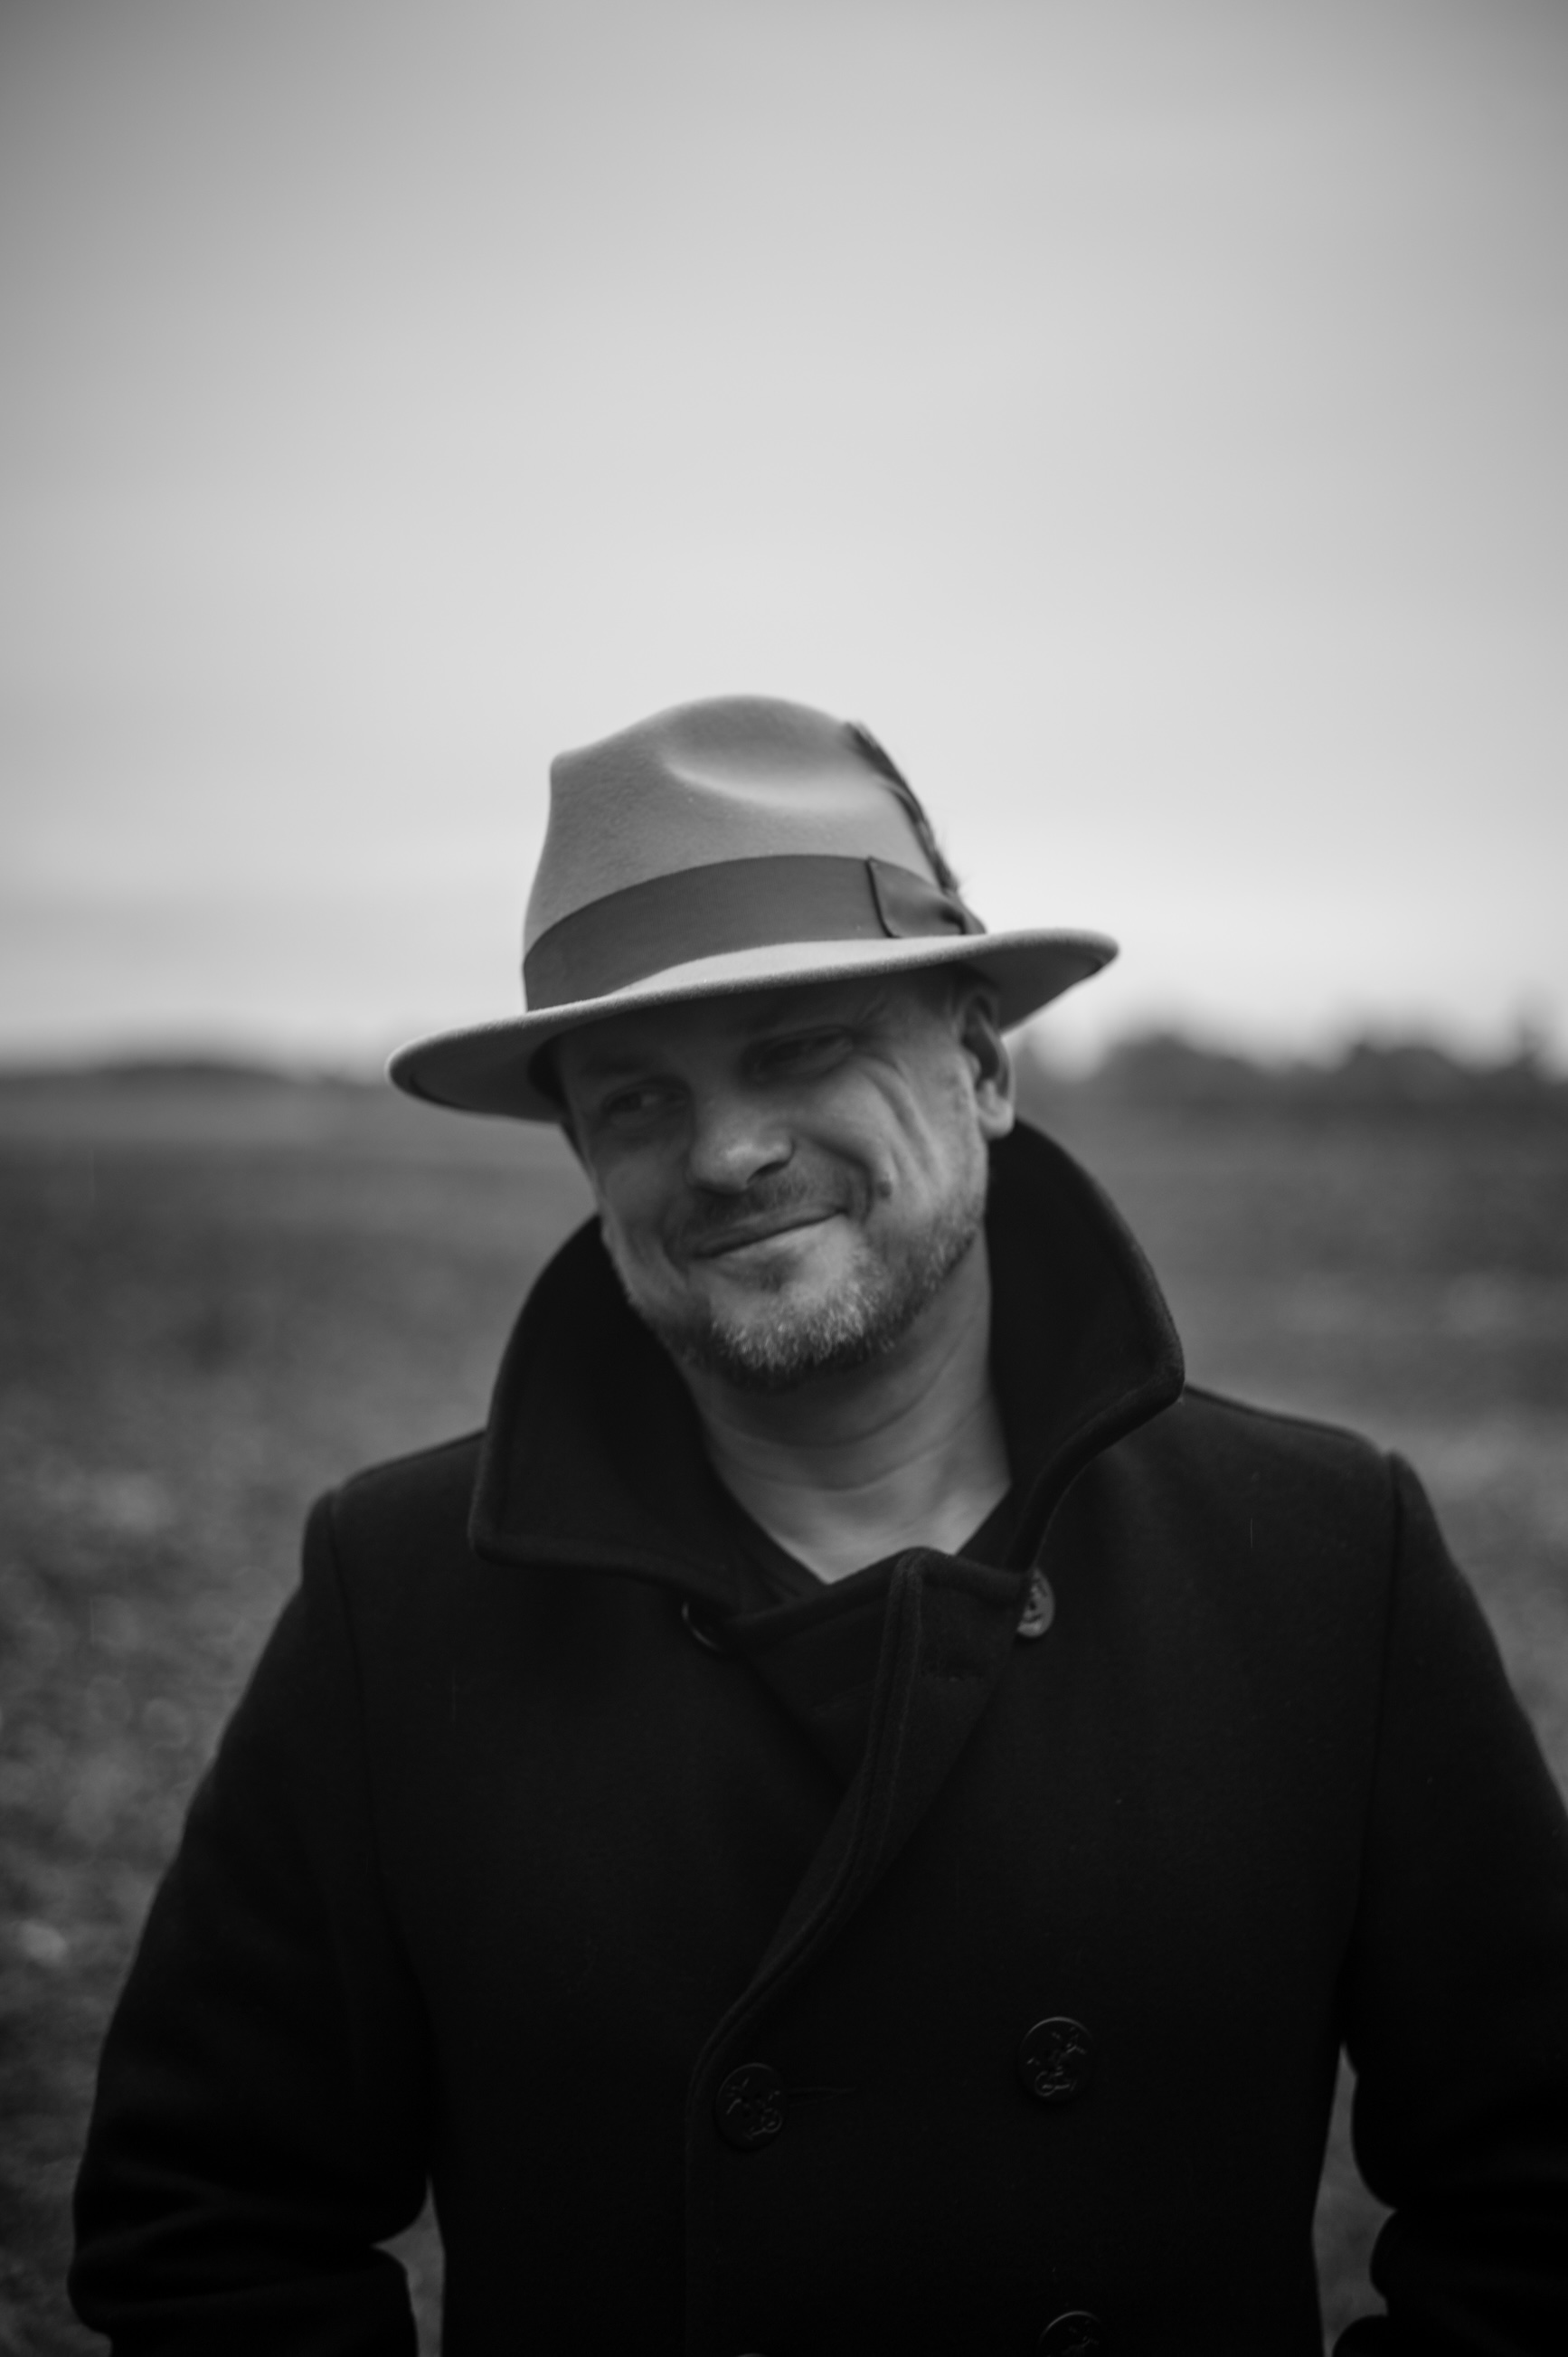
Sebastien (Seba) Deleersnyder, co-founder and CTO of Toreon, combines software engineering expertise with a passion for holistic product security. After earning his Master’s in Software Engineering from the University of Ghent, he became a driving force in the security community as founder of the Belgian OWASP chapter, OWASP Foundation Board member, and co-founder of BruCON, Belgium’s annual security conference. His leadership of OWASP SAMM and decade-long role as a highly-rated Black Hat trainer have significantly impacted global software security.
linkedin.com

2024

Daniel Cuthbert

Daniel Cuthbert

Distinguished Lifetime Members · 2024
From the early days of OWASP, Daniel has been on a relentless quest to build software so secure that even he might struggle to hack it (but don’t count on it). Self-diagnosed with an obsession for bugs and offensive operations, he’s turned his penchant for poking holes into a crusade for making vendors shape up. By channeling his mischief into the ASVS and other cunning initiatives, he’s been plotting to save the software world—one responsible vendor at a time.
linkedin.com
Martin Knobloch

Martin Knobloch

Distinguished Lifetime Members · 2024
2006: Attending my first OWASP AppSec conference, the OWASP AppSec in Belgium (and only missed two since) 2007: Joining the OWASP Netherlands Chapter Board 2008: First time presenting at an OWASP conference, the OWASP Australia Security Conference at Gold Coast, Queensland, Australia 2008: Chairing the OWASP Education committee, as result of attending the first OWASP Summit in Portugal 2009: Co-organizing the first OWASP BeNeLux-Day, and all of them since 2010: First active involvement in an OWASP AppSec conference, hosting the CTF in Sweden 2011: Co-organizing the OWASP Summit 2011 2015: Conference Chair of the OWASP Global AppSec EU in Amsterdam 2017: Joining the OWASP Global Foundation Board of DIrectors, until 2022 2019: Joining the OWASP Europe Board Over the years, I have been promoting, mentoring and supporting OWASP in general; the various projects, chapters and events. The leaders, organizers, members and volunteers. Anyone trying to find their way into AppSec.
linkedin.com
Riotaro OKADA

Riotaro OKADA

Distinguished Lifetime Members · 2024
Executive Director of Asterisk Research, Inc., OWASP Lifetime Member, a Japan Chapter Lead, Contributor, MBA, CISA, CSA holder
linkedin.com
Tanya Janca

Tanya Janca

Distinguished Lifetime Members · 2024

Tanya Janca, aka SheHacksPurple, is the best-selling author of ‘Alice and Bob Learn Secure Coding’, ‘Alice and Bob Learn Application Security’ and ‘Cards Against AppSec’. Over her 28-year IT career she has won countless awards (including OWASP Lifetime Distinguished Member and Hacker of the Year), spoken all over the planet, and is a prolific blogger. Tanya has trained thousands of software developers and IT security professionals, via her online academies (We Hack Purple and Semgrep Academy), and her live training programs. Having performed counter-terrorism, led security for the 52nd Canadian general election, developed or secured countless applications, Tanya Janca is widely considered an international authority on the security of software.
linkedin.com

Page 1 of 2 · 3 years per page

Other OWASP awards

OWASP Logo
OWASP is a nonprofit foundation improving software security through open-source projects, global communities, and education. All resources are free and open to everyone.
OWASP, the OWASP logo, and Global AppSec are registered trademarks and AppSec Days, AppSec California, AppSec Cali, SnowFROC, OWASP Boston Application Security Conference, and LASCON are trademarks of the OWASP Foundation, Inc.
© 2026, OWASP Foundation Inc. All rights reserved.